Operational resilience
Keep access to critical functions continuously visible and open to review.
Reconciliation, segregation of duties, privileged-access governance and non-human identity ownership provide live evidence for the access-control aspects of ICT risk management.
- Control
- Observation
- Evidence
- Gap
The controls
The evidence for each control
For each control you see what the policy requires and which evidence an auditor can inspect.
1
Continuous reconciliation
Every run timestamps the comparison between expected and actual access.
2
Critical and third-party access
Contractor, partner, machine and privileged access carry ownership and expiry.
3
Control evidence
Framework-cited packs draw from live review, reconciliation and incident history.
4
Operational safety
Safety limits and a pause switch let you stop unexpected changes.
The evidence, in the product
Watch the evidence being produced
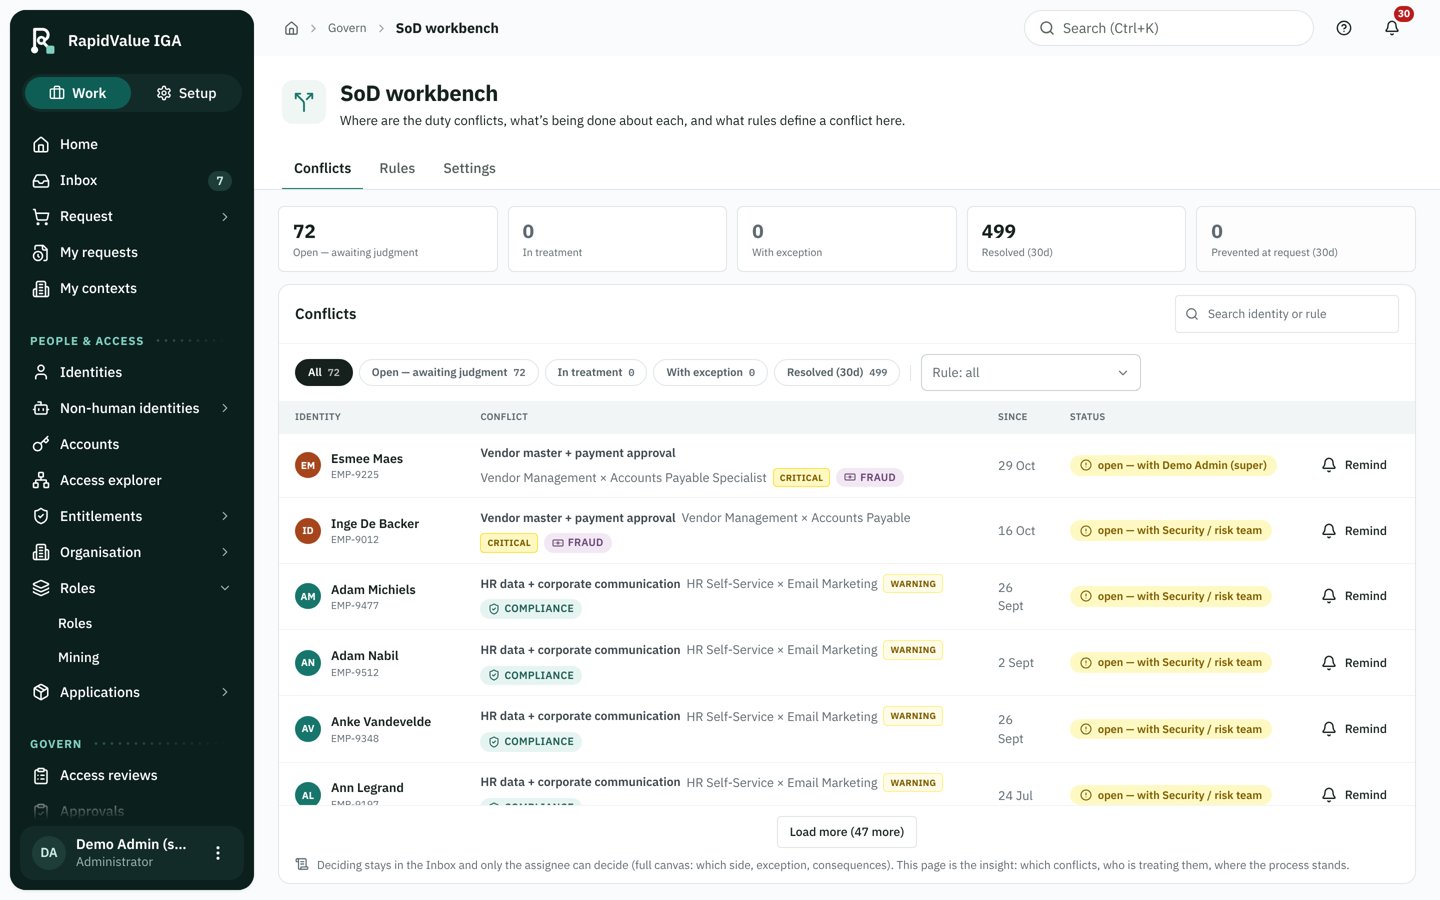
Conflicting access to critical functions, found across systems and flagged before it is granted.
What this does not cover
DORA covers far more than identity governance. RapidValue addresses specific access-governance and evidence controls.