Access-control accountability
Show how you control privileged and machine access over time.
Continuous certification, owners for machine identities, event evidence and privileged-access controls support the documented access oversight expected from essential and important entities.
- Control
- Observation
- Evidence
- Gap
The controls
The evidence for each control
For each control you see what the policy requires and which evidence an auditor can inspect.
1
Access policy and review
Define who should have access, and review it on a schedule or after a relevant event.
2
Privileged-access coverage
Track eligibility, elevation, expiry and break-glass follow-up.
3
Machine identity ownership
Identify critical non-human identities and give each one an owner.
4
Unmeasured stays unmeasured
Where a connector cannot observe a control such as MFA state, it is shown as unmeasured.
The evidence, in the product
Watch the evidence being produced
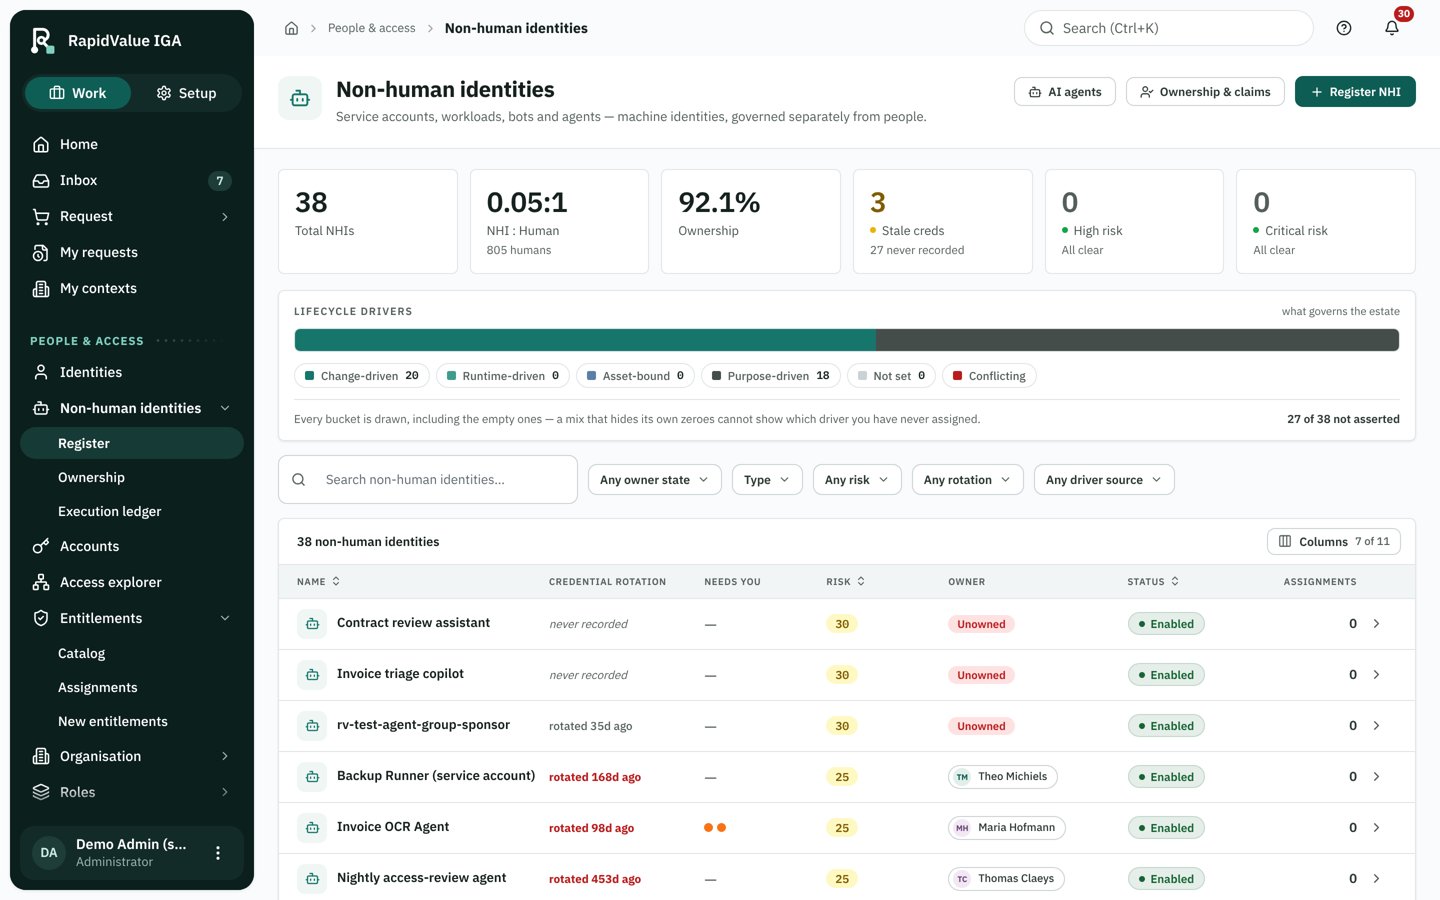
Service accounts and AI agents with an accountable owner, a purpose and a kill switch on the record.
What this does not cover
RapidValue contributes identity-governance controls. It is not a complete NIS2 programme or a certification.