Control evidence
See access decisions, reviews and exceptions next to the control they support.
Segregation of duties, certification, privileged access and a history that cannot be changed provide the evidence auditors commonly request for internal-control and information-security reviews.
- Control
- Observation
- Evidence
- Gap
The controls
The evidence for each control
For each control you see what the policy requires and which evidence an auditor can inspect.
1
SOX · internal controls
Segregation-of-duties rules, approval trails and point-in-time access evidence support control testing.
2
ISO 27001 · access control
Ownership, review, lifecycle and privileged-access evidence map to the relevant control set.
3
Evidence windows
Generate a pack for the exact review period and inspect it before download.
4
Independent verification
Signed exports and file hashes let an auditor detect tampering without using the product.
The evidence, in the product
Watch the evidence being produced
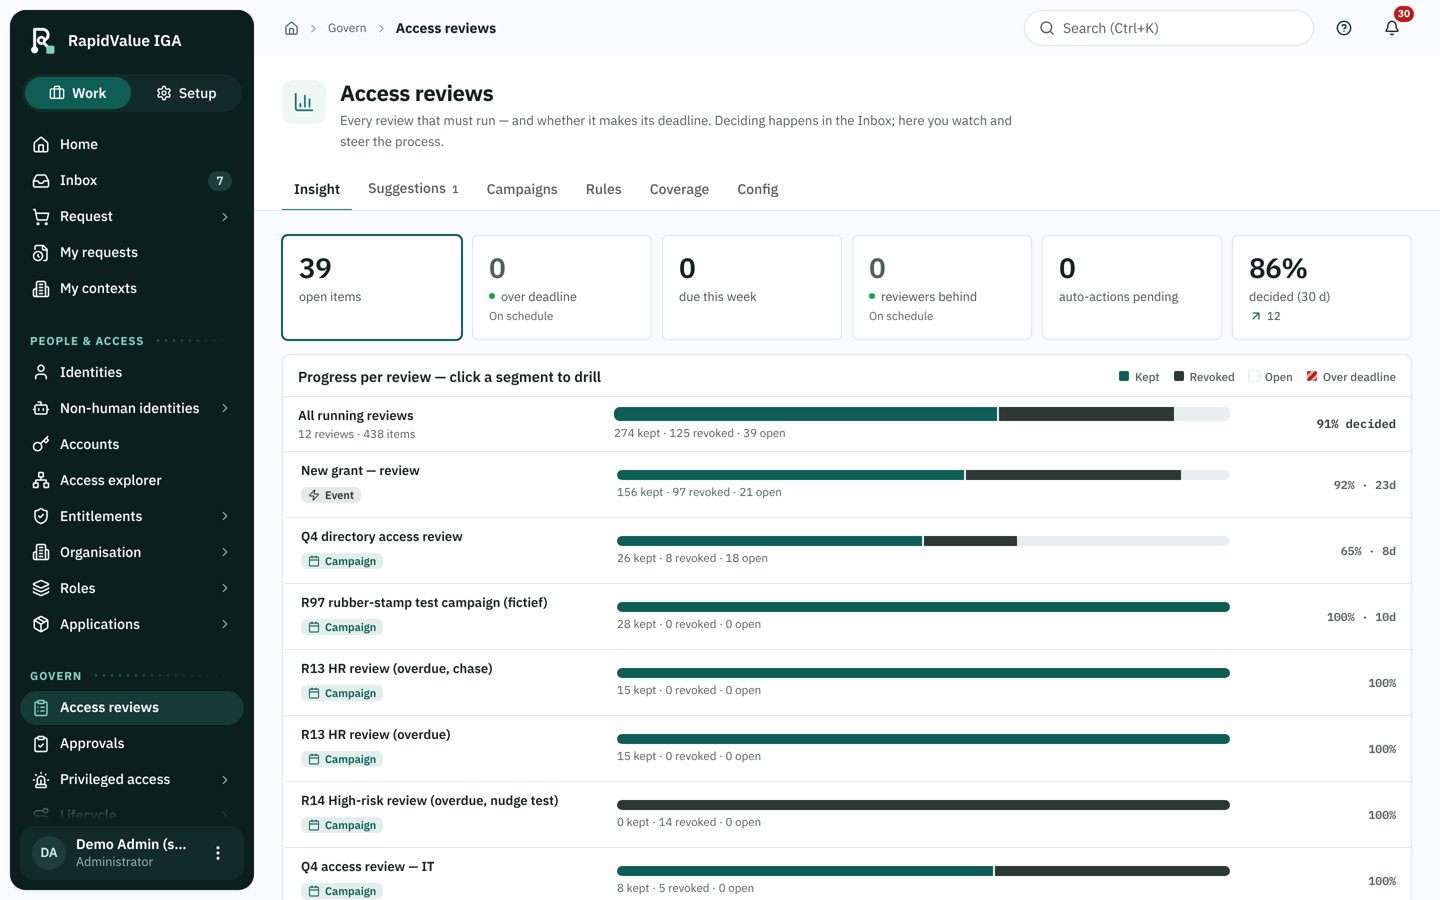
Managers review their own team’s access person by person, with the context and the decision trail.
What this does not cover
RapidValue holds no SOX, ISO 27001 or SOC 2 certification today. Evidence packs are not audit opinions.